Kali Linux in Forensic Science: Uses and Applications
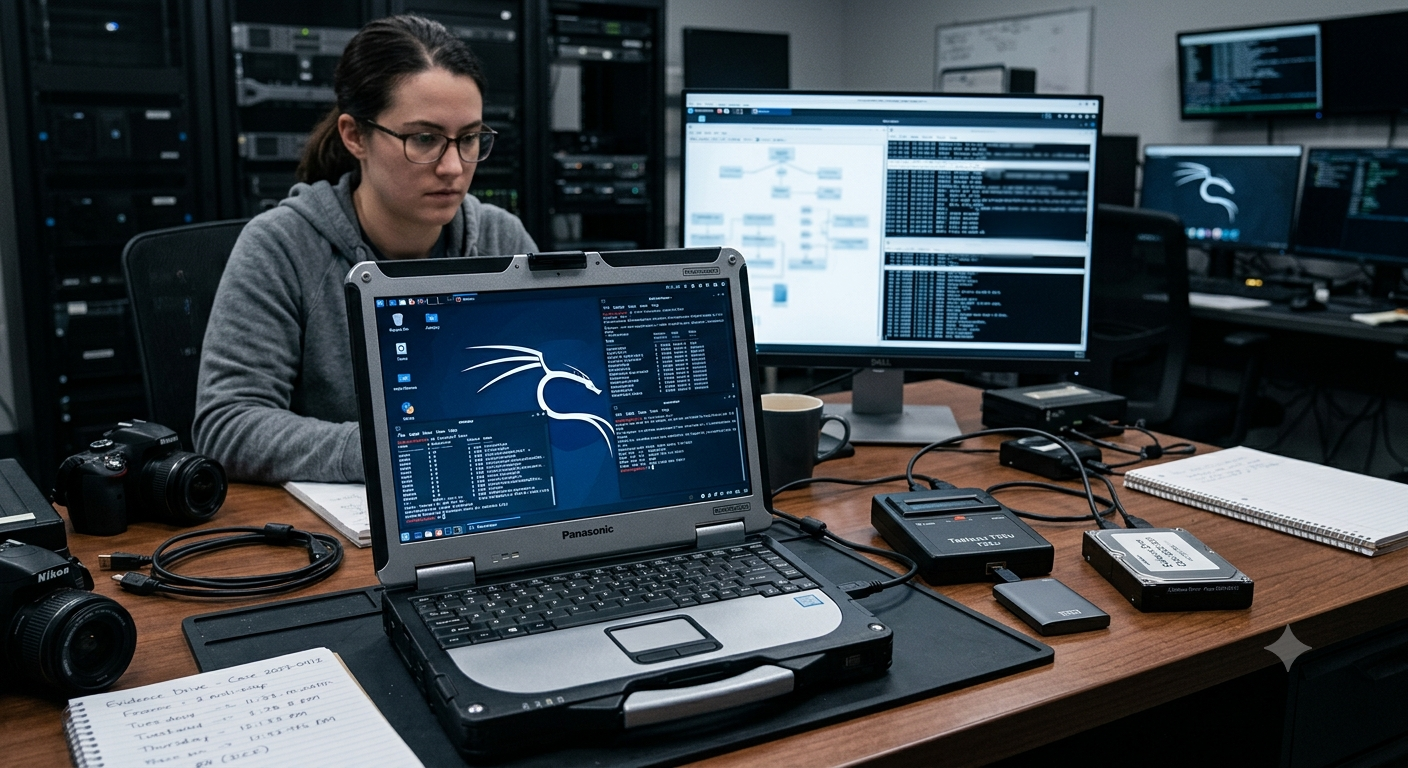
Kali Linux in forensic science has become a useful topic for digital forensic professionals, cybersecurity researchers, students, and investigators working with digital evidence. Although Kali Linux is widely associated with penetration testing and cybersecurity, its collection of open-source tools can also support several activities involved in digital forensics and forensic investigation.
From examining storage devices and file systems to analyzing network traffic, metadata, memory images, and system logs, Kali Linux provides a flexible environment for working with different types of digital evidence. When used with appropriate forensic procedures, it can complement dedicated forensic platforms and help investigators perform specialized technical examinations.
What Is Kali Linux?
Kali Linux is a Debian-based Linux distribution developed for cybersecurity, penetration testing, security research, digital forensics, and related technical activities.
One of its major advantages is the large collection of security and investigation utilities available within its ecosystem. This makes Kali Linux useful for professionals who need command-line tools, scripting capabilities, network-analysis utilities, file-analysis tools, and other technical resources.
However, it is important to understand that Kali Linux is a tool environment, not a complete forensic methodology. The reliability of a forensic examination depends on proper evidence handling, acquisition, preservation, validation, documentation, and interpretation.
1. Disk and Storage Examination
One of the important applications of Kali Linux in forensic science is the examination of digital storage media.
Computers, external hard drives, USB drives, memory cards, and other storage devices may contain evidence relevant to an investigation. Linux utilities can help an examiner inspect disk structures, partitions, file systems, directories, and files.
Depending on the examination requirements, investigators may work with forensic images rather than directly interacting with the original evidence.
Storage examination may involve:
-
Identifying partitions and file systems
-
Examining directory structures
-
Searching for relevant files
-
Examining file properties
-
Identifying hidden or suspicious files
-
Examining deleted-file remnants
-
Working with forensic disk images
These capabilities can be useful during the examination and triage of large volumes of digital evidence.
2. File and Metadata Analysis
Digital files may contain information that is not immediately visible to a normal user. This information is commonly referred to as metadata.
Metadata may provide details about a file’s creation, modification, software, device, or other characteristics, depending on the file format and the information retained within it.
Tools such as ExifTool can assist forensic examiners in examining metadata from photographs, videos, documents, and other file types.
For example, during a digital forensic examination, an investigator may examine an image for available information about the camera, timestamps, software, or other embedded attributes.
Metadata should always be interpreted carefully because it can be modified, removed, or affected by file transfers and software processing.
3. Deleted Data and File Recovery
Another area where Kali Linux in forensic science can be useful is deleted-data examination.
When a user deletes a file, the data may not immediately disappear from the storage medium. Depending on the file system, device type, subsequent activity, and storage technology, remnants of deleted information may remain available for examination.
Forensic tools can assist investigators in searching for and recovering certain types of deleted information.
Potentially recoverable information may include:
-
Documents
-
Photographs
-
Videos
-
Archives
-
Temporary files
-
File-system remnants
However, recovery is not guaranteed. SSDs, for example, may behave differently from traditional hard disk drives because of technologies such as TRIM. Therefore, the type and condition of the storage device should always be considered before attempting recovery.
4. Hashing and Digital Evidence Integrity
Maintaining evidence integrity is a fundamental part of digital forensics.
Cryptographic hashing allows an examiner to generate a digital value representing a particular file, dataset, or forensic image. Commonly used algorithms include SHA-256 and, in some legacy environments, MD5.
Kali Linux provides command-line utilities that can be used to calculate hash values.
For example, an examiner may calculate a hash during evidence acquisition and later calculate it again to verify whether the relevant data has changed.
A simplified workflow may look like:
Evidence → Acquisition → Hash Calculation → Examination → Verification
Hash values are therefore an important component of documenting digital evidence and verifying data integrity.
5. Network Forensics
Digital investigations can also involve network evidence.
Network traffic captured during a lawful investigation can contain information about communications between devices, services, and systems. Kali Linux provides access to various networking and packet-analysis utilities.
Wireshark, for example, can be used to examine packet-capture files and investigate network communications.
An examiner may analyze information such as:
-
IP addresses
-
Network protocols
-
DNS requests
-
Connection patterns
-
Communication timestamps
-
File-transfer activity
-
Network sessions
Network analysis can provide additional context when investigating unauthorized access, suspicious communications, malware incidents, or other digital events.
6. Memory Forensics
Some digital evidence exists only temporarily in a computer’s volatile memory, or RAM.
When a system is running, RAM may contain information relating to processes, network connections, loaded modules, command activity, and other system states.
Memory forensic frameworks such as Volatility can be used to analyze acquired memory images.
Kali Linux can provide a convenient environment for running command-line memory-analysis tools and frameworks.
Memory analysis can be particularly useful in investigations involving:
As with other forensic evidence, investigators should document how the memory image was acquired and maintain appropriate integrity controls.
7. Searching Large Digital Evidence Sets
Modern forensic examinations can involve enormous quantities of data. A single computer or external storage device may contain thousands or even millions of files.
Manually examining every file can be extremely time-consuming.
Linux command-line utilities can help investigators perform targeted searches based on:
-
File names
-
File extensions
-
Keywords
-
Directory locations
-
Timestamps
-
File characteristics
Tools such as find and grep can assist with specific search tasks.
For example, an examiner investigating a case may search a forensic dataset for relevant names, email addresses, URLs, file extensions, or case-specific keywords.
This type of targeted searching can make the initial examination process more efficient.
8. Log and System Artifact Examination
Operating systems and applications generate various logs and system artifacts that can help establish what happened on a device.
Depending on the operating system and application, investigators may examine:
-
Authentication events
-
System events
-
Application logs
-
Network activity
-
Device connections
-
Configuration changes
-
User activity
Kali Linux provides a flexible environment for examining text-based logs and processing datasets using command-line utilities and scripts.
However, investigators should understand the origin and limitations of each artifact before drawing conclusions from it. Time zones, system-clock settings, log rotation, missing records, and user or system modifications can all affect interpretation.
9. Forensic Automation and Scripting
A significant advantage of Linux-based environments is the ability to automate repetitive forensic tasks.
Python, Bash, and other scripting technologies can assist with activities such as:
Automation can save time when an investigator needs to process a large volume of evidence.
Nevertheless, automated results should be validated. A script can assist an examiner, but it should not replace forensic methodology, verification, or professional interpretation.
10. Open-Source Tools in Digital Forensics
Another advantage of Kali Linux in forensic science is its access to the wider open-source cybersecurity ecosystem.
Open-source tools can be useful for education, research, tool validation, laboratory experimentation, and specialized forensic examinations.
They can also complement commercial forensic platforms when a particular technical capability is required.
However, an important distinction should be made: open-source does not automatically mean forensic-grade.
Before relying on a particular tool in a formal investigation, forensic professionals should understand its capabilities and limitations and, where appropriate, validate its results against known datasets or established forensic procedures.
Kali Linux and the Digital Forensic Process
Kali Linux can support different stages of a digital investigation, but it should be used within a structured forensic workflow.
A simplified digital forensic process can include:
Identification → Preservation → Acquisition → Examination → Analysis → Documentation → Reporting
During these stages, investigators should maintain proper documentation and evidence-handling procedures.
Where appropriate, examination should be performed using verified forensic copies or images rather than unnecessarily modifying original evidence.
The specific tools used will depend on the evidence source and investigative objective.
Kali Linux Compared With Dedicated Forensic Platforms
Kali Linux should not automatically be considered a replacement for dedicated forensic platforms.
Professional digital forensic laboratories may use specialized solutions such as EnCase, Magnet AXIOM, FTK, Autopsy, Cellebrite, Oxygen Forensics, and other tools depending on the type of evidence being examined.
Kali Linux can instead function as a complementary technical environment.
For example, a forensic examiner may use a dedicated forensic platform for evidence acquisition and artifact analysis while using Linux-based utilities for a specialized examination, scripting task, metadata analysis, network analysis, or independent validation.
The appropriate tool depends on the evidence, examination objective, validation requirements, and reporting standards.
Why Kali Linux Is Useful for Forensic Professionals
The flexibility of Kali Linux makes it particularly valuable for professionals who want to understand the technical side of digital evidence.
It can help forensic practitioners develop practical knowledge of:
For students and forensic trainees, working with Kali Linux can also provide a practical understanding of how different digital evidence sources can be examined.
This technical knowledge can complement practical training in computer forensics, mobile forensics, and digital forensic examination.
Conclusion
The applications of Kali Linux in forensic science extend beyond its well-known cybersecurity and penetration-testing capabilities. Its collection of open-source tools can support several areas of digital forensic work, including disk examination, metadata analysis, deleted-data investigation, hashing, network forensics, memory analysis, log examination, evidence searching, and automation.
Its flexibility makes it a useful supporting environment for forensic professionals, researchers, students, and cybersecurity practitioners working with digital evidence.
However, a forensic examination is not defined by the software being used. Proper evidence preservation, validated acquisition, integrity verification, documentation, repeatability, and competent interpretation remain essential.
When used responsibly and combined with an appropriate forensic methodology, Kali Linux in forensic science can provide investigators with a flexible technical environment for examining and understanding digital evidence.
Post comments (0)