What Information Do Email Headers Contain?
Introduction
An email may look like a simple message containing a sender, recipient, subject, and timestamp. However, behind this visible information is a larger set of technical data known as the email header.
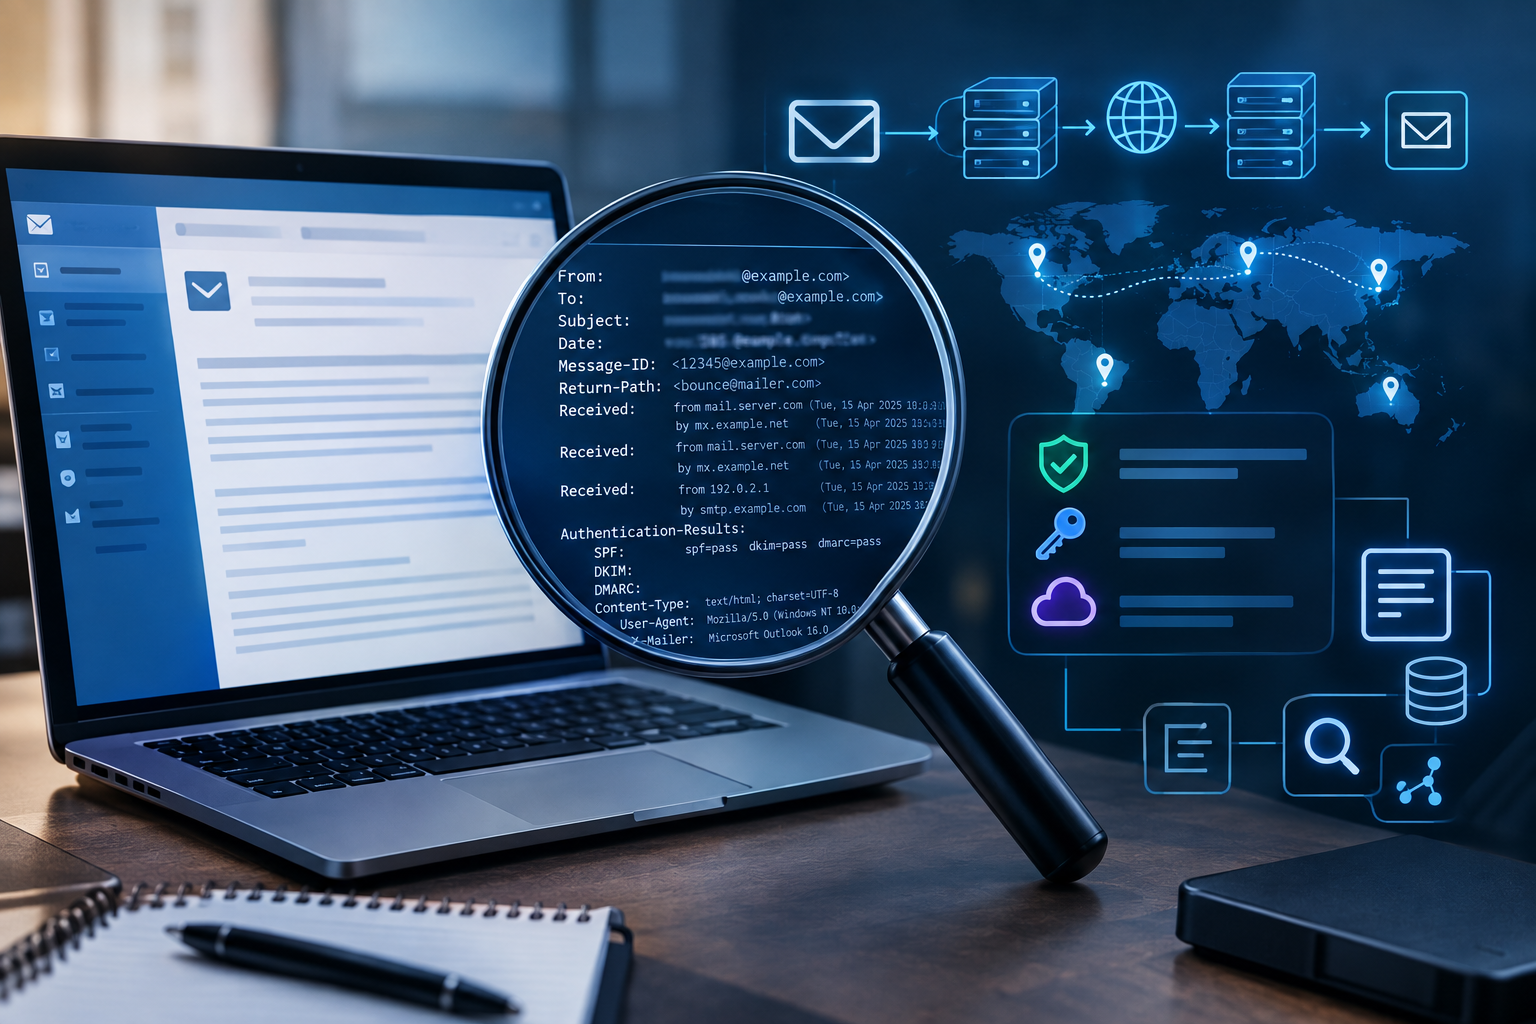
In digital forensics, email headers can provide valuable information about how an email was transmitted, which mail servers handled it, when different stages of delivery occurred, and whether certain authentication mechanisms were successful.
This makes email headers an important source of digital evidence in investigations involving phishing, spoofing, business email compromise, cyber harassment, fraud, and other email-related incidents.
However, email headers must be interpreted carefully. An IP address or server entry does not automatically identify the person who sent an email. Investigators need to examine the complete header and correlate its information with other evidence.
What Is an Email Header?
An email header is a collection of metadata attached to an email message.
Unlike the email body, which contains the actual message visible to the recipient, header information is primarily used by mail systems to route, deliver, authenticate, and process the message.
Some header fields are visible in ordinary email interfaces, such as:
Other technical fields may only become visible when the user selects options such as “Show Original,” “View Source,” or “View Message Headers.”
A complete email header can contain many fields depending on the email provider, mail server, security system, and route taken by the message.
What Information Can Email Headers Contain?
1. Sender and Recipient Information
Common fields include:
From: Indicates the address presented as the sender.
To: Identifies the intended recipient.
Cc: Shows additional recipients who were copied on the message.
Reply-To: Specifies the address to which replies should be directed.
These fields are useful during an investigation, but they should not automatically be treated as proof of the sender’s identity. The address displayed in the From field, for example, can potentially be spoofed.
2. Date and Time Information
The Date header generally contains the date and time associated with the message.
Other timestamps can appear in the Received fields added by mail servers. These can help investigators reconstruct the sequence in which an email moved through different systems.
Investigators should consider time zones, server configurations, clock differences, and timestamp reliability when interpreting this information.
3. Received Headers
The Received field is one of the most important components of email forensics.
As an email passes through mail infrastructure, receiving mail servers commonly add their own Received entries. A message can therefore contain multiple entries describing its movement between systems.
These entries may provide information about:
- Mail servers involved in delivery
- IP addresses
- Hostnames
- Connection methods
- Timestamps
- The sequence of mail-server transfers
Investigators commonly examine the Received chain from the bottom upward when reconstructing the route of a message.
However, not every entry necessarily represents the original sender’s device. Different entries may have been added by different systems along the delivery path.
4. IP Addresses
Email headers may contain IPv4 or IPv6 addresses associated with servers or network connections.
An IP address can help investigators determine which network or service handled a particular connection. It may also help identify whether multiple messages passed through the same infrastructure.
However, an IP address generally identifies a network endpoint or service, not automatically an individual person.
The address could belong to a corporate network, cloud provider, VPN, proxy, hosting service, residential ISP, or email infrastructure.
Additional records may therefore be required to associate an IP address with a particular subscriber or user.
5. Message-ID
The Message-ID field contains an identifier associated with an email message.
Forensic investigators can use Message-ID values to help:
- Correlate copies of the same message
- Compare messages from different sources
- Investigate email threads
- Identify relationships between messages
- Support timeline reconstruction
The format of Message-ID values varies between systems, so its structure should not be treated as definitive proof of where an email originated.
6. Return-Path
The Return-Path field is associated with the address used for handling delivery failures, often referred to as the envelope sender.
It can differ from the address displayed in the From field.
This distinction can be useful when examining suspicious messages because the visible sender and the underlying mail-delivery information may not match.
7. Authentication Results
Modern email systems use several mechanisms to verify whether messages are authorized to use a particular domain.
Important mechanisms include:
- SPF — Sender Policy Framework
- DKIM — DomainKeys Identified Mail
- DMARC — Domain-based Message Authentication, Reporting & Conformance
Authentication results may appear in a field such as:
Authentication-Results
For example, a header may contain results indicating whether SPF, DKIM, or DMARC checks passed or failed.
SPF allows a domain owner to specify which servers are authorized to send email on its behalf.
DKIM uses a cryptographic signature to help verify that certain parts of a message have not been altered after signing and that the message was signed using a domain-associated key.
DMARC builds on SPF and DKIM and provides domain-level policies and alignment checks.
These results can provide useful evidence when investigating suspected spoofing. However, an authentication result does not independently prove the identity of the human sender.
8. MIME and Content Information
Email headers can also contain information about how the message content is structured.
For example, Content-Type may indicate whether the message contains plain text, HTML, or multiple components.
Other information may relate to:
- Character encoding
- Attachments
- Inline content
- Multipart message structure
This can become relevant when examining suspicious attachments or malicious email content.
9. User-Agent and X-Headers
Some email clients and mail systems may add fields such as User-Agent or X-Mailer.
These may sometimes provide information about the software used to compose or process an email.
Mail systems can also add custom X- fields containing information related to spam filtering, security systems, mail gateways, message tracking, or internal processing.
Such fields should be treated as supporting evidence and interpreted in context.
Can Email Headers Reveal the Sender’s Location?
This is a common misconception in email investigations.
An email header may contain an IP address, but that does not necessarily reveal the sender’s exact physical location.
The address may correspond to:
- A mail server
- Cloud infrastructure
- A VPN
- A proxy
- An ISP
- A corporate network
- A webmail service
IP geolocation can provide an approximate geographic association, but it should not be interpreted as the exact physical location of the sender.
Attribution generally requires correlation with additional evidence.
Can Email Headers Be Forged?
Yes. Certain portions of an email header can potentially be manipulated because some fields are controlled by the sending system or email client.
This is why investigators should distinguish between information supplied by the sender or sending application and information added by receiving mail infrastructure.
For example, a suspicious From: field should not automatically be considered evidence of the actual sending system.
Similarly, the presence of an IP address does not automatically establish that the device associated with that address originated the email.
How Are Email Headers Examined in Digital Forensics?
A typical forensic examination may involve several stages.
Step 1: Preserve the Original Email
The original email should be preserved in a manner that maintains its available metadata. Screenshots alone are generally insufficient because they do not preserve the underlying email structure.
Step 2: Obtain the Complete Header
The investigator should obtain the complete header rather than relying only on information displayed in the normal email interface.
Depending on the email service, options may include View Source, Show Original, or View Headers.
Step 3: Examine Relevant Fields
Investigators can examine fields such as:
- Received
- Message-ID
- From
- Return-Path
- Reply-To
- Authentication-Results
- SPF
- DKIM
- DMARC
- Date
- MIME information
Step 4: Reconstruct the Mail Path
The available Received information can be examined to understand how the message moved through different email systems.
Step 5: Correlate With Other Evidence
Email-header analysis becomes more useful when combined with other evidence, including:
- Server logs
- Mailbox records
- Authentication logs
- DNS information
- ISP records
- Device artifacts
- Browser artifacts
- Related emails
- Cloud-service records
The goal is to build a defensible sequence of events rather than simply identify an IP address.
Email Header Analysis in Investigations
Email-header examination can contribute to several types of investigations.
Phishing: Headers may help determine whether an email claiming to originate from an organization passed through infrastructure associated with that domain.
Business Email Compromise: Investigators can examine authentication results, routing information, and message identifiers when investigating suspicious business communications.
Email Spoofing: Differences between visible sender information and authentication or routing information may provide indicators of spoofing.
Cyber Harassment: Header information can contribute technical evidence when investigating repeated or threatening communications.
Fraud: Email metadata can help establish relationships between messages, accounts, infrastructure, and timelines.
Important Limitations
Email headers are valuable, but they are not a standalone attribution mechanism.
Investigators should consider several limitations:
- Header fields can be manipulated.
- Cloud email services may not expose the original connection information.
- Shared infrastructure can make individual attribution difficult.
- VPNs and proxies can affect the apparent origin.
- Authentication results require proper interpretation.
- Different systems may record timestamps differently.
For these reasons, forensic conclusions should be based on the totality of available evidence.
Conclusion
Email headers contain much more information than the sender, recipient, and subject visible in a typical inbox.
Fields such as Received, Message-ID, Return-Path, Authentication-Results, SPF, DKIM, and DMARC can provide important technical information about the processing and transmission of an email.
At the same time, email-header analysis has limitations. An IP address is not automatically a person’s identity, a displayed sender is not necessarily the true sender, and an authentication result does not independently establish who physically sent a message.
Proper preservation, technical interpretation, and correlation with other digital evidence are therefore essential.
For digital forensic examiners, understanding email headers is an important skill because seemingly small pieces of metadata can become significant when reconstructing the events surrounding an email-related incident.
Post comments (0)